
Identify what needs protecting
Identify information, obligations and interfaces.
ISO/IEC 27001:2022 / IMPLEMENTED IN PROJECT WORKFLOW
Information is part of every idea we build. Its protection belongs in the brief, the decisions, the delivery and the handover.
Open the working handbookHOW THE PROJECT MOVES
Identify information, obligations and interfaces.
Assess risk and approve necessary treatment.
Apply access, supplier and development controls.
Review control evidence and release authority.
Test recovery and maintain agreed security ownership.
THE IMPLEMENTATION BOUNDARY
This security handbook turns the selected requirement areas into responsibilities for the commissioned service. Its agreed scope identifies information, interfaces, participating organisations and the controls justified by risk assessment. These are original operating procedures; the published standard remains the authoritative requirements source.
This handbook maps the project workflow to ISO/IEC 27001:2022, including the 2024 climate-action amendment. Clause references identify that edition.
Standard edition and background: ISO’s official standard page .
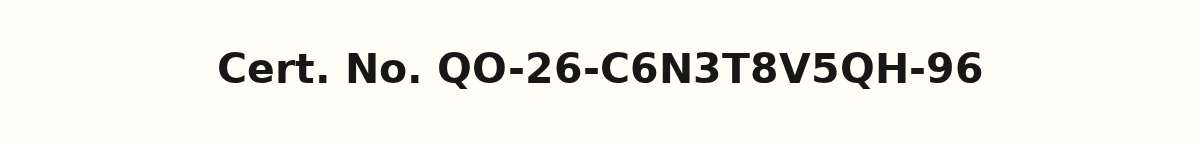
The supplied reference identifies a management system within its certified activities. For an information-security engagement, the applicable certification edition and scope must be checked alongside the information boundary and selected safeguards. The working handbook connects that boundary to risk decisions, operating controls and review.
FROM REQUIREMENT TO PRACTICE
Use these security chapters to trace a requirement into a risk decision, an assigned responsibility and evidence that the chosen measure operates. Begin at the information boundary or jump to the control decision your service needs to resolve.
CLAUSE 4 / THE PROJECT HANDBOOK
Information has a purpose, a place and people who depend on it.
The security lead identifies the organisation’s information, services, technology, threats and operating constraints. Climate-related disruption is assessed for relevance to continuity, suppliers and physical working locations rather than presumed irrelevant to digital work.
The project records requirements from clients, staff, users, suppliers and relevant authorities, then determines which the security system addresses. Contractual confidentiality, data-handling instructions and relevant climate expectations are linked to an owner.
The security scope identifies services, locations, people, assets and interfaces included in the engagement. External hosting and client systems are mapped with responsibilities, so an outsourced component does not create an unexplained gap.
Risk assessment, access, supplier decisions, incident response, release and recovery operate as a connected management process. Their interactions and evidence are maintained so protection continues through the whole delivery lifecycle.
CLAUSE 5 / THE PROJECT HANDBOOK
Care for information requires authority, time and a route to act.
Leadership allocates resources and ensures security requirements are part of planning and delivery. Exceptions and significant risks reach an authorised decision maker; delivery pressure does not silently override information obligations.
The security policy defines the project’s direction, objectives and commitment to applicable requirements and improvement. It is controlled, communicated to contributors and made available to interested parties as appropriate.
Roles identify who administers access, assesses risk, approves releases, manages incidents and reviews system performance. Reporting routes and deputies are established without publishing sensitive technical details on the public website.
CLAUSE 6 / THE PROJECT HANDBOOK
A control earns its place by addressing a real exposure.
The team identifies risks and opportunities affecting the security system’s intended outcomes. Actions are integrated into delivery and checked for effectiveness, with attention to changes in services, suppliers, information and responsibilities.
An agreed method defines acceptance criteria and a consistent assessment approach. Risk owners identify confidentiality, integrity and availability exposures, assess consequences and likelihood, determine levels and prioritise treatment using the same criteria.
The team chooses treatment options and necessary controls, checks Annex A for omissions and records inclusion, implementation status and justified exclusions in the Statement of Applicability. Risk owners approve the treatment plan and accept remaining risk explicitly.
Security objectives fit the policy, relevant requirements and assessment results. Each has an owner, resources, timing and evaluation approach; for example, the agreed recovery objective is tested rather than inferred from a backup file’s existence.
A new hosting service, supplier, integration or working arrangement is planned before changing the security system. Ownership, risk effects, dependent controls and the evidence needed to confirm the new arrangement are considered together.
CLAUSE 7 / THE PROJECT HANDBOOK
Protection includes working knowledge, careful communication and dependable records.
The project allocates appropriate people, secure working tools, review capacity and recovery facilities for the defined scope. Resource limitations are made visible before they undermine a selected control or agreed obligation.
Relevant competence is checked for development, administration, data handling and security review. Training or supervised work addresses gaps, and evidence shows whether the intervention enabled the person to perform the task safely.
Contributors understand the policy, their security contribution and the consequences of missing a requirement. Briefings cover confidential inputs, approved sharing, suspicious activity and how to report a concern promptly.
The communication plan defines security information, recipients, timing, responsible people and channels. Incident communications follow agreed authority and applicable duties; the public site is never used to disclose credentials or exploitable configuration.
The system holds the information needed by the standard and by effective operation: scope, policy, risk method, applicability, treatment, evidence and reviews. Detail follows scope and complexity while protecting sensitive material.
Security records identify their author, date, version and format. New policies, assessments and operating instructions are reviewed and approved before becoming the current basis for access or technical decisions.
Authorised people can retrieve current records, while access, distribution, changes, retention and disposal are controlled. External documents are identified and retained evidence is protected from accidental loss, inappropriate disclosure or unapproved alteration.
CLAUSE 8 / THE PROJECT HANDBOOK
Risk assessment becomes a practical delivery and operating routine.
The delivery plan turns treatment decisions into operating criteria and checks. Changes and external services are controlled, unexpected deviations are assessed, and records show that necessary activities happened before the service was released.
Security risk assessment is repeated at planned intervals and when significant changes occur. A new data flow, authentication method or provider prompts review before deployment; assessment results are retained with the affected scope.
Approved treatment actions are implemented and their results recorded. An unfinished measure remains visible with an owner and decision; it is not presented as operating simply because it appears in the design or procurement brief.
CLAUSE 9 / THE PROJECT HANDBOOK
Monitoring, audit and leadership review ask different, complementary questions.
The team defines what security performance and system effectiveness need measuring, the method, timing and responsible people. Results such as recovery exercises, access reviews and incident follow-up are evaluated with valid, repeatable methods.
Internal audit examines conformity with the organisation’s security arrangements and relevant standard requirements, alongside effective operation. It looks for evidence across risk decisions, actual controls and improvement rather than treating a policy as proof.
The audit programme considers process importance and earlier findings. Scope and criteria are defined, reviewers preserve objectivity, reports reach relevant management and records retain both the programme and its results.
Management reviews the system at planned intervals for continued suitability, adequacy and effectiveness. The meeting considers whether the security arrangements still fit the project portfolio and operating environment.
Inputs include previous actions, context and stakeholder changes, feedback, progress against objectives, performance trends, audit results and corrective work. Risk assessments, treatment progress and improvement opportunities provide a basis for decisions about resources and priorities.
Management decides on improvements and necessary changes to the security system. Decisions are retained with responsible owners and follow-up, so the next review can judge progress and unresolved exposure.
CLAUSE 10 / THE PROJECT HANDBOOK
Protection improves when problems change the way the next project runs.
Feedback, monitoring, audit and management review drive continuing improvements in suitability, adequacy and effectiveness. Useful changes may simplify access administration, strengthen supplier checks or make recovery evidence easier to repeat.
A security nonconformity is controlled and its consequences addressed. Causes and similar exposures are examined, corrective actions are applied, their effectiveness is reviewed and the system is changed where needed; the event, actions and outcomes remain recorded.
ANNEX A / FOUR CONNECTED THEMES
The reference set contains 93 controls across four themes. It is not a promise that every control is required for every project. Necessary controls come from risk treatment and relevant obligations; the Statement of Applicability explains selection, status and justified exclusions. Additional controls can be necessary.
Information classification, approved sharing, supplier obligations, cloud use, incident responsibilities and continuity arrangements are selected against the project’s actual risks.
Examples to consider: A.5.9 asset inventory; A.5.15 access policy; A.5.19 supplier relationships; A.5.23 cloud services; A.5.24 incident preparation; A.5.30 ICT continuity readiness.
Role-appropriate screening, confidentiality expectations, awareness, remote working and changes in responsibility support safe participation. Access is adjusted when somebody joins, changes role or leaves.
Examples to consider: A.6.3 awareness and training; A.6.5 responsibilities after role changes; A.6.6 confidentiality agreements; A.6.7 remote working; A.6.8 reporting security events.
Workspaces, equipment and media are considered alongside the commissioned provider’s facilities. Desk arrangements, secure storage and disposal are proportionate to what is handled; responsibility for provider facilities is checked through supplier assurance.
Examples to consider: A.7.4 physical monitoring; A.7.7 clear desks and screens; A.7.9 assets away from premises; A.7.10 storage media; A.7.14 equipment disposal or reuse.
Necessary controls can include least-privilege access, approved authentication, vulnerability handling, secure configuration, backups, logging and secure development. Their configuration is verified in the relevant environment without disclosing sensitive settings publicly.
Examples to consider: A.8.8 vulnerability management; A.8.9 configuration; A.8.13 backups; A.8.15 logging; A.8.25 development lifecycle; A.8.28 secure coding; A.8.31 separation of environments; A.8.32 change management.
Control structure: ISO/IEC SC 27, control-framework overview . The examples above are project interpretations; applicability is established in the project record.
CARE YOU CAN FOLLOW
Tell us which information the proposed service needs and who should be allowed to use it. We can establish its boundary, examine the risks and agree the evidence required before a protected workflow is released.